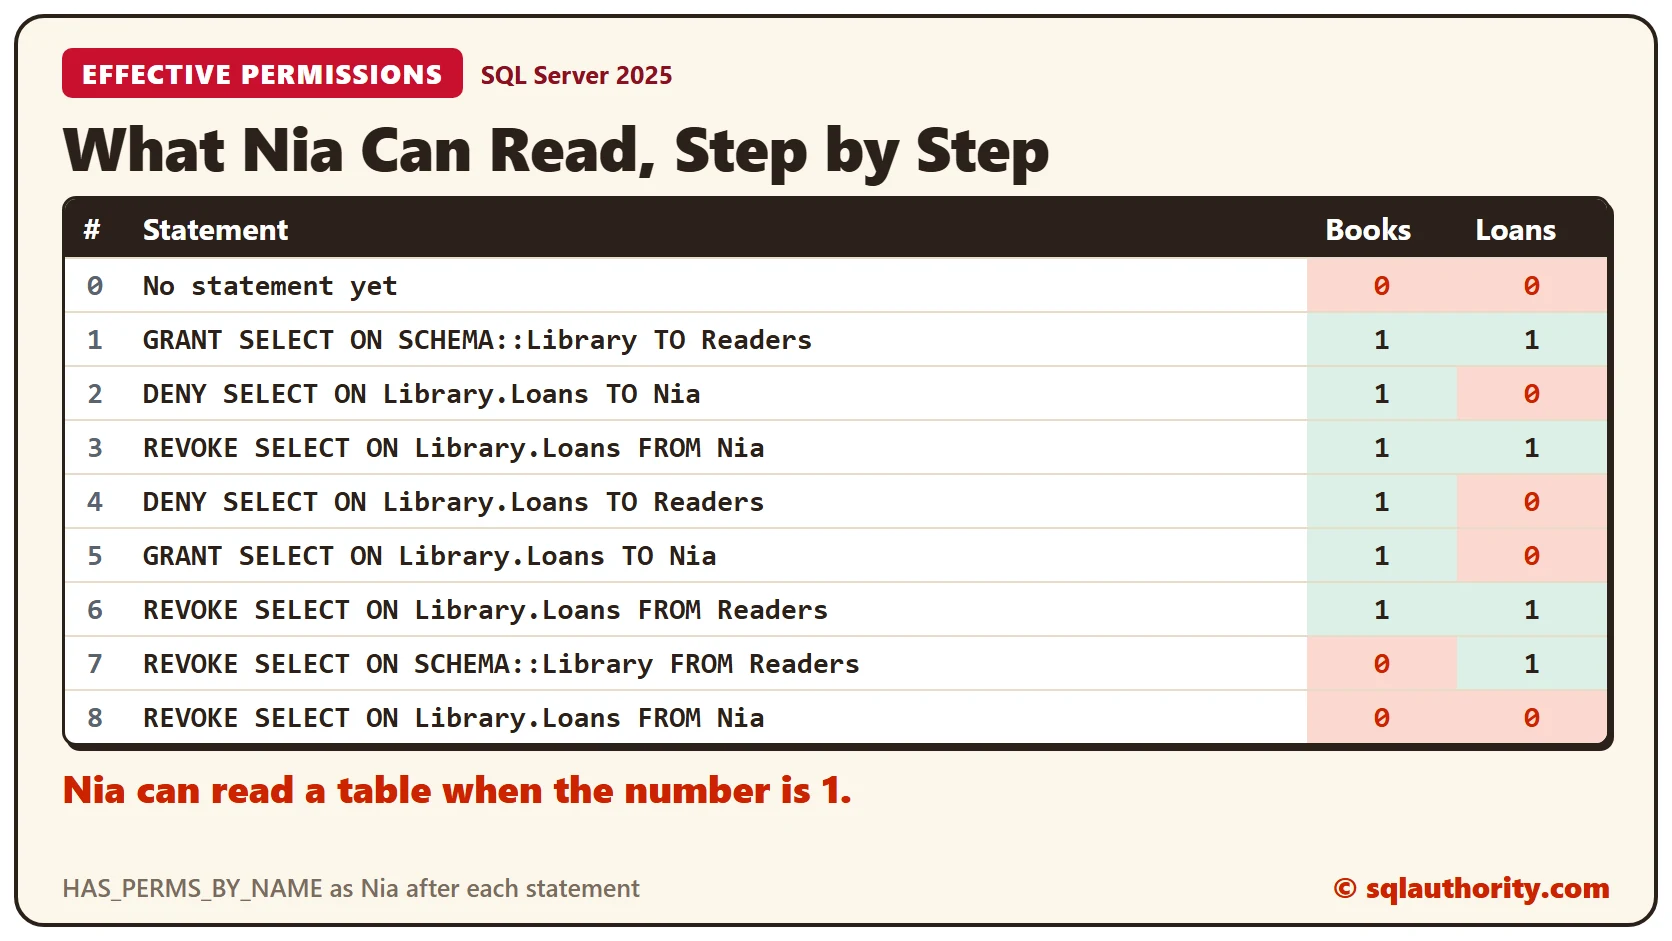
Effective permissions are what a user can do after every GRANT, DENY and REVOKE has been added together. This post follows one user through eight statements, with a role, a direct DENY and a direct GRANT, and checks the result after each step with HAS_PERMS_BY_NAME. It then shows how to take away one ability from a user who holds CONTROL. Every result comes from SQL Server 2025.
Securables and Principals in SQL Server: Who Gets Which Permission
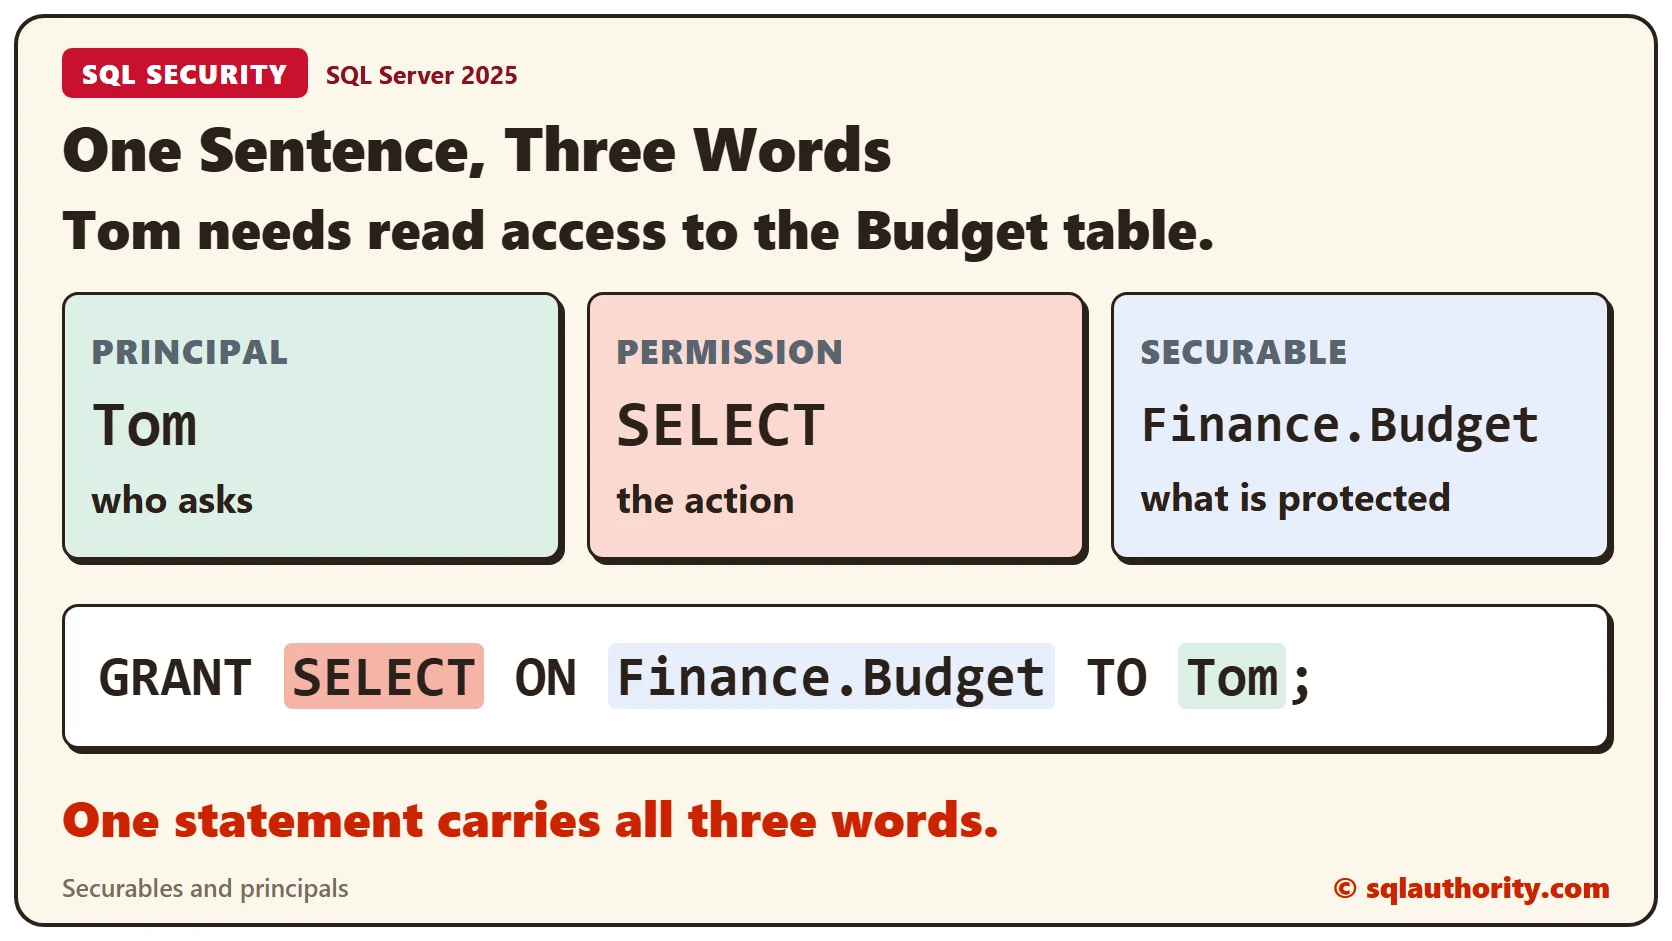
Securables and principals are the two nouns of SQL Server security, and a permission joins them. This post gives a user named Tom access to a Finance table, then uses GRANT, DENY and REVOKE and reads the permission list after each step. It ends with one grant on a whole schema. Every result comes from SQL Server 2025.
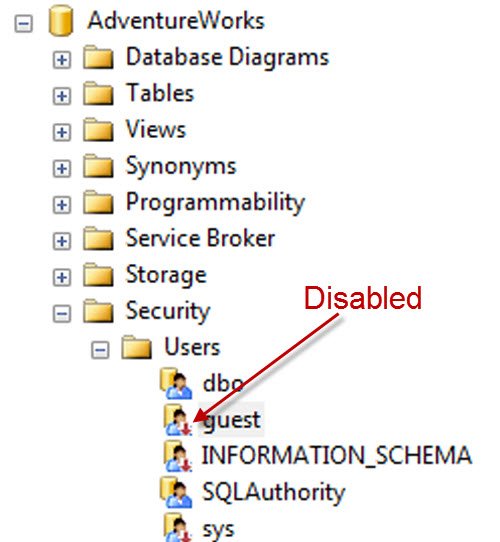
SQL SERVER – Detecting guest User Permissions – guest User Access Status
Is the guest user enabled or disabled, and what is the default? I answer reader questions and show ways to detect guest user access status.
SQL SERVER – Disable Guest Account – Serious Security Issue
I like to disable guest account access in SQL Server unless there is a real need for it. Here is why the guest user can be a serious security issue.