

Login failed, not associated with a trusted SQL Server connection? I hit it between SQL Server 2008 and 2005 and fixed it with a matching Windows user.
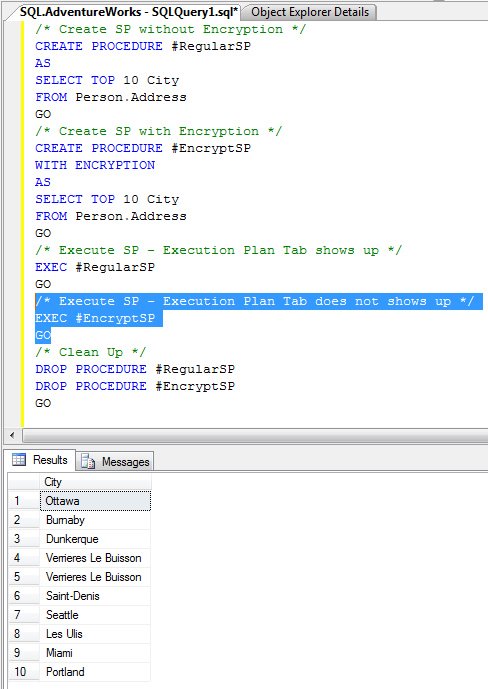
SQL SERVER – Stored Procedure WITH ENCRYPTION and Execution Plan
Here is what I found about WITH ENCRYPTION and execution plan: an encrypted SP hides its actual execution plan too. Two sample SPs show it.

SQL SERVER – Transaction and Local Variables – Swap Variables – Update All At Once Concept
Two ideas with examples: transactions have no effect on local variables, and an UPDATE applies all its changes at once, which lets you Swap Variables in one go.
SQL Injection: The Joke, the Failure and the Parameter Fix
SQL Injection makes a good joke and a terrible incident. The tests here show a concatenated query returning every row for one hostile name, the same text passed as a parameter returning none, a table name caught by QUOTENAME, and a read-only user blocked from dropping a table.
Renaming or Disabling the sa Login
Renaming or disabling the sa login requires a dependency inventory, tested alternate admin access, and monitoring after the change.

Responding to a SQL Server Security Bulletin
A SQL Server Security Bulletin should trigger exposure checks, ordered patching, verified recovery, and a clear management update.
SQL SERVER – Guidelines and Coding Standards Complete List Download
My coding standards complete list for SQL Server, cut to what people follow: naming, formatting, and the rules that prevent real bugs.