
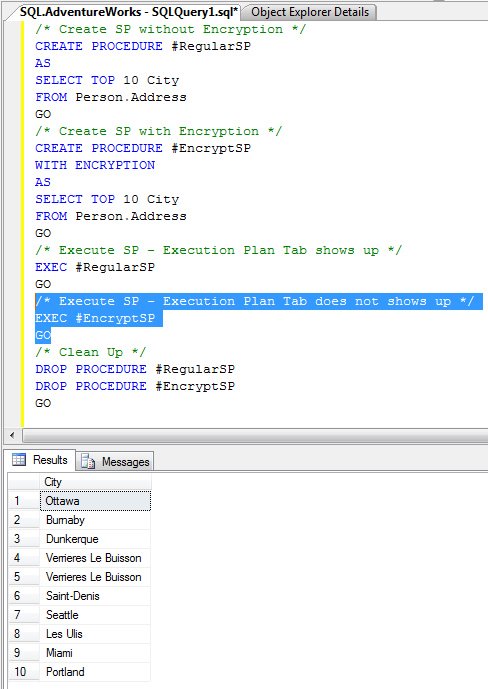
Here is what I found about WITH ENCRYPTION and execution plan: an encrypted SP hides its actual execution plan too. Two sample SPs show it.
Sharing an Execution Plan Without Exposing Sensitive Data
Protect sensitive data when sharing an execution plan by inspecting XML values, redacting names and literals, and checking the file again.

SQL SERVER – Transaction and Local Variables – Swap Variables – Update All At Once Concept
Two ideas with examples: transactions have no effect on local variables, and an UPDATE applies all its changes at once, which lets you Swap Variables in one go.

SQLAuthority News – SQL Injection – SQL Joke, SQL Humor, SQL Laugh
The SQL Injection cartoon readers sent me many times, finally on the blog. Plus a demo of how dynamic SQL opens the door to it, and a way to close it.
Renaming or Disabling the sa Login
Renaming or disabling the sa login requires a dependency inventory, tested alternate admin access, and monitoring after the change.

Responding to a SQL Server Security Bulletin
A SQL Server Security Bulletin should trigger exposure checks, ordered patching, verified recovery, and a clear management update.
SQL SERVER – Guidelines and Coding Standards Complete List Download
My coding standards complete list for SQL Server, cut to what people follow: naming, formatting, and the rules that prevent real bugs.