
Kevin Hazzard explains common sense data security for sensitive user information, with humor and real world examples you will recognize.
SQL SERVER – Validation Rules: Code or Database? – Notes from the Field #054
Should validation rules live in the .NET app layer or in the database? G. Andrew Duthie looks at this common argument between developers and DBAs.

SQL SERVER – Using Bitwise And (&) Instead of a Junction Table – Notes from the Field #053
Stuart Ainsworth shows a cool trick: using Bitwise And (&) instead of a junction table to get more performance with fewer code changes.
Linked Server Logins: Stop Mapping Everyone to sa
Audit linked server logins for blanket remote sysadmin mappings, test with a low-privilege identity, and replace broad access safely.
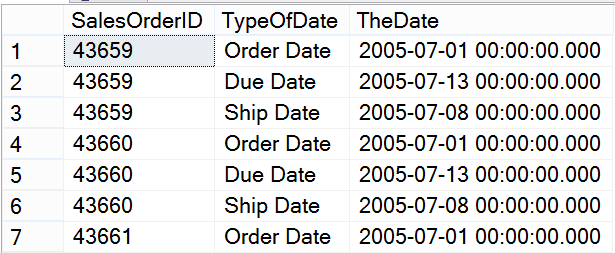
SQL SERVER – Beginning Table Valued Constructors – Notes from the Field #052
Kathi Kellenberger explains Table Valued Constructors, a relatively unknown topic, in the 52nd episode of my Notes from the Field series.
Audit Triggers That Record the Real User Behind EXECUTE AS
Your audit table says dbo for every change, and nobody can tell who really did it. Here is how to capture the person behind EXECUTE AS.
Extended Security Updates Explained
Extended Security Updates give eligible older SQL Server releases limited critical security coverage while you complete a migration.