
At a Pluralsight booth, a DBA from the banking world asked me many SQL Server security questions. Here are my notes from those security conversations.
SQL SERVER – One Trick of Handling Dynamic SQL to Avoid SQL Injection Attack?
SQL Injection is not a SQL Server problem, it comes from coding habits. Here is one trick of handling dynamic SQL to avoid SQL injection attack on a search page.

SQL SERVER – Invoking a Stored Procedure from Azure Mobile Services – Notes from the Field #066
Can you call a SQL stored procedure from Azure Mobile Services? In Notes from the Field #066, Kevin Hazzard shows how, with a bit of humor along the way.

SQL SERVER – The DBA goes to MARS – Maintenance, Architecture, Research and Support – Notes from the Field #063
Stuart Ainsworth tells a captivating story on why the DBA goes to MARS: Maintenance, Architecture, Research and Support, the proactive side of the job.

SQL SERVER – How to Find Weak Passwords Using T-SQL?
After a hacker got in through the sysadmin account, a reader asked for help. Here is how to find weak passwords for SQL logins using T-SQL.
OPENROWSET vs Linked Servers: Querying Another Server Safely
Compare OPENROWSET and linked servers, inspect login mappings, keep filtering remote, and review authentication and encryption before use.
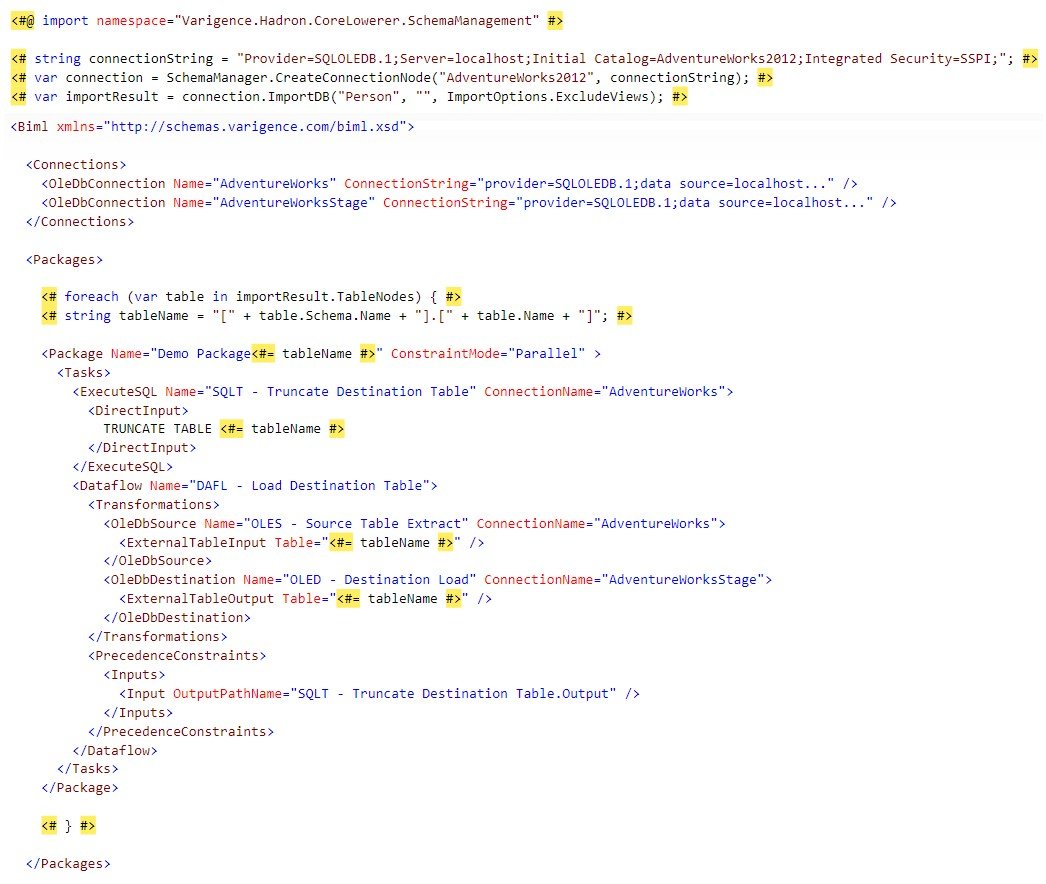
SQL SERVER – Iterating over Metadata with BimlScript – Notes from the Field #061
Reeves Smith continues his Biml series and shows how iterating over metadata with BimlScript helps automate repetitive SQL Server BI work.