
Claude on SQL Server is safe when production gives it eyes and nothing else. This post splits the loop into three stages: start this week with a read-only login, make it a daily habit with a past cases library, then run it on a schedule with a second opinion. I tested the login on SQL Server 2025.
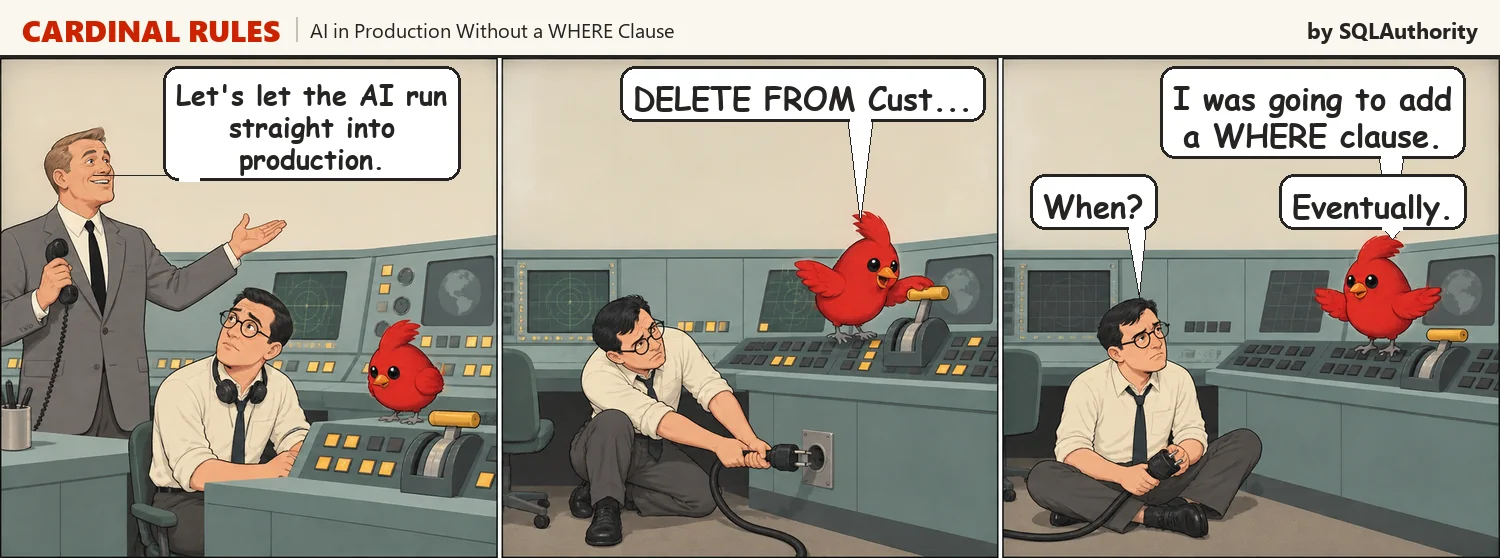
AI in Production Without a WHERE Clause
AI in production without a second pair of eyes is a quick way to lose a table. Cardinal was going to add the WHERE clause. Eventually.
SQL SERVER – Implementing Row-Level Security (RLS)
Row-Level Security (RLS) in SQL Server enables fine-grained control over data access, ensuring users can only view or modify rows pertinent to their roles or responsibilities.
SQL SERVER – Dynamic Data Masking (DDM) Introduction
Dynamic Data Masking (DDM) in SQL Server is a feature that helps protect sensitive data by masking it from unauthorized users.

SQL Server Ledger – Are You Really Using This Feature?
SQL Server Ledger – has taken data integrity to the next level, integrating blockchain-style data verification directly into the database.

Letting an LLM Query SQL Server Safely: A Read-Only Login and Guardrails
Let an LLM query SQL Server through a restricted login, approved views, enforced row filtering, execution limits, and query auditing.

SQL SERVER – Understanding Grant, Deny, and Revoke Permissions
These aspects are the fundamental building blocks of SQL Server security management. Let us understand Grant, Deny, and Revoke Permissions.