
SQL Vulnerability Assessment was available in older SSMS releases. My walkthrough used SSMS 17.4 with SQL Server 2012 or later.
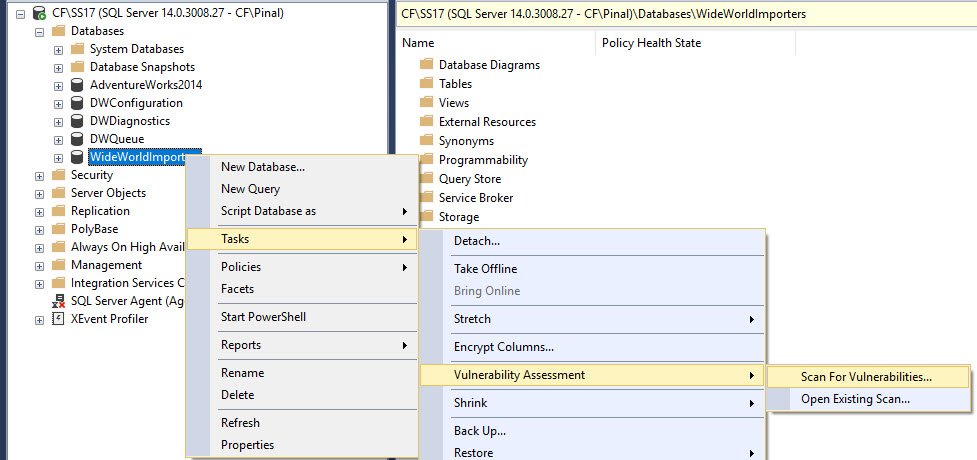
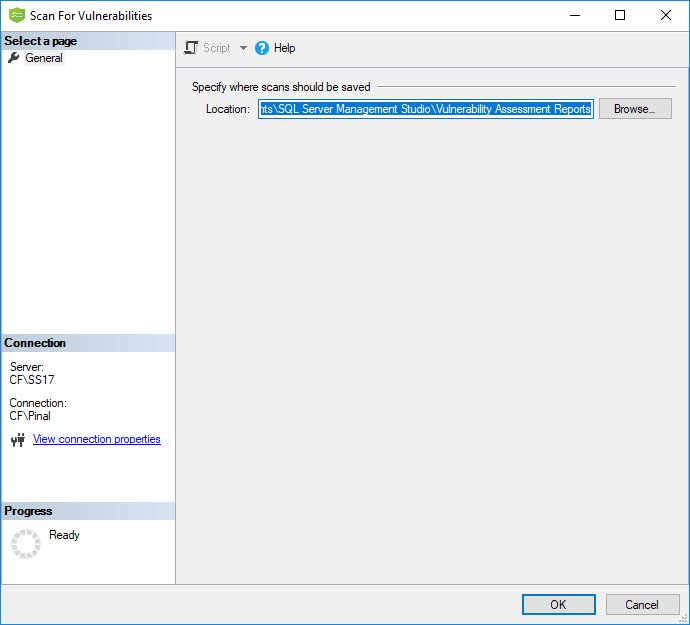
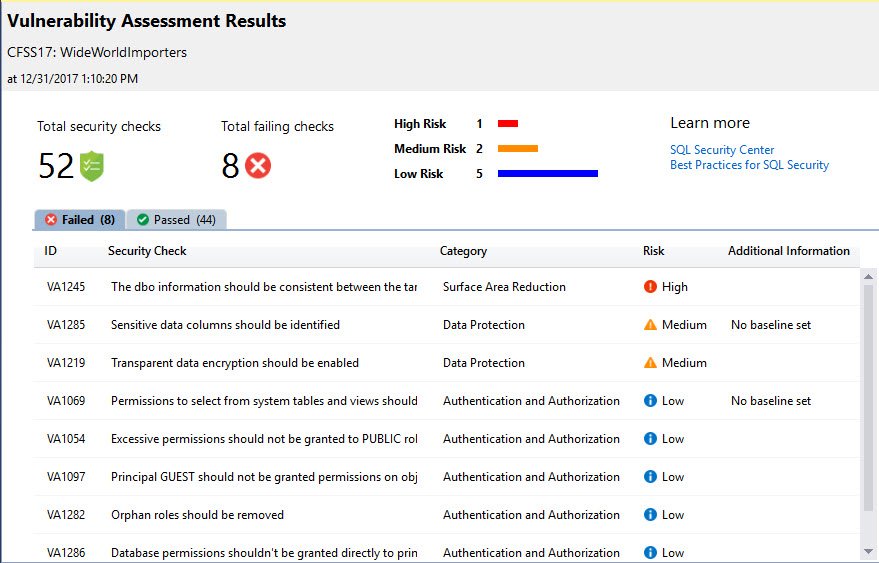
That database menu exposed Tasks > Vulnerability Assessment > Scan for Vulnerabilities. The user selected a report location and reviewed high, medium and low risk findings. Opening a check showed its assessment and suggested remediation.
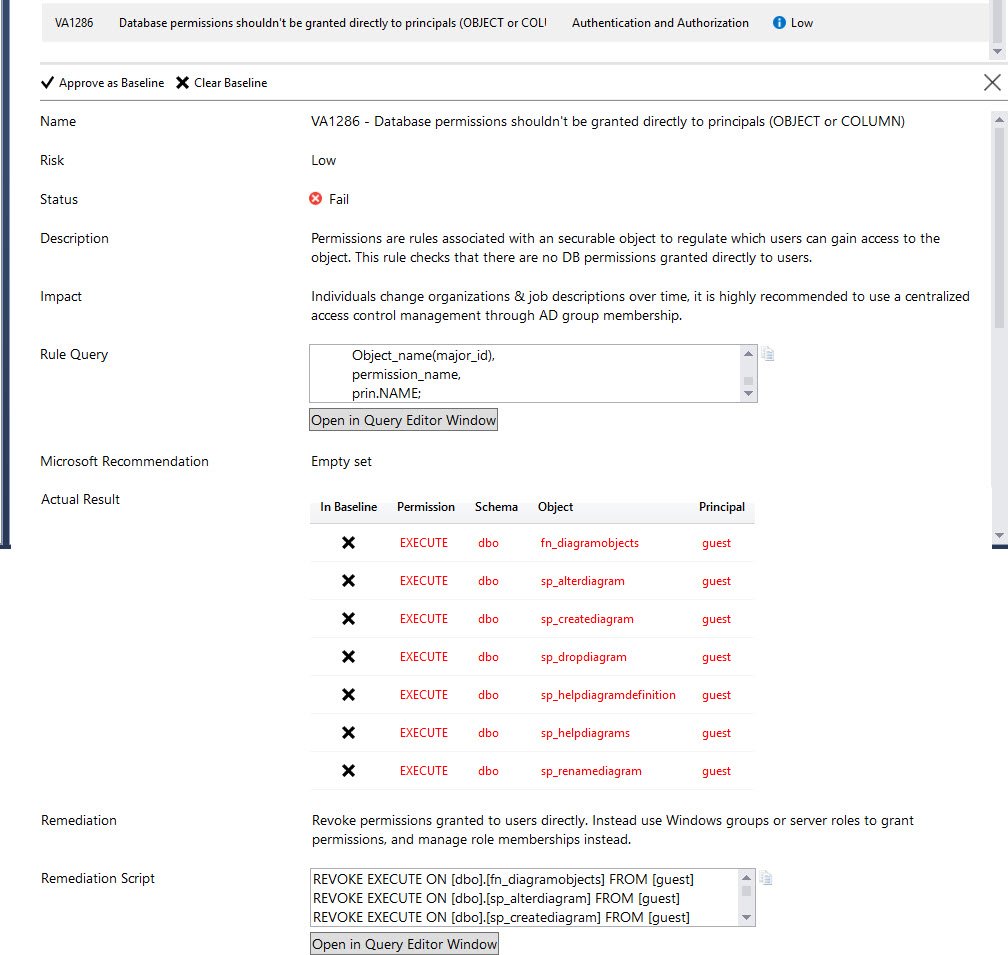
SSMS removed this feature in version 19.1. A newer SSMS installation doesn’t restore that menu. Microsoft directs current assessment toward Defender for SQL. Choose the supported option for the deployment.
I investigate findings against an agreed baseline. Suggested remediation can affect permissions, applications and operations. Don’t apply every recommendation blindly. A clean scan doesn’t establish that every vulnerability or compliance requirement has been addressed.
A vulnerability scan is not a compliance certificate, it is evidence for investigation and remediation.
Published by Pinal Dave on SQLAuthority. More of my work at pinaldave.com.
Discover more from SQL Authority with Pinal Dave
Subscribe to get the latest posts sent to your email.


3 Comments. Leave new
Hi Dave, it’s possible export this report? I see that from SSMS export only in json format…
tnx
Is there a detailed downloadable list for everything that can be detected?
Is there a list of all VA findings that are possible that has definitions and how to fix them notes?